
Foundation, the corporate behind the Passport {hardware} pockets, has reported a safety incident that occurred on the twenty sixth of November.
Here, the attackers despatched greater than 23,000 phishing electronic mail makes an attempt utilizing emails that appeared to return from official Foundation domains.
These emails have been designed to trick customers into revealing their pockets restoration phrases, which gave attackers entry to the cryptocurrency saved of their wallets.
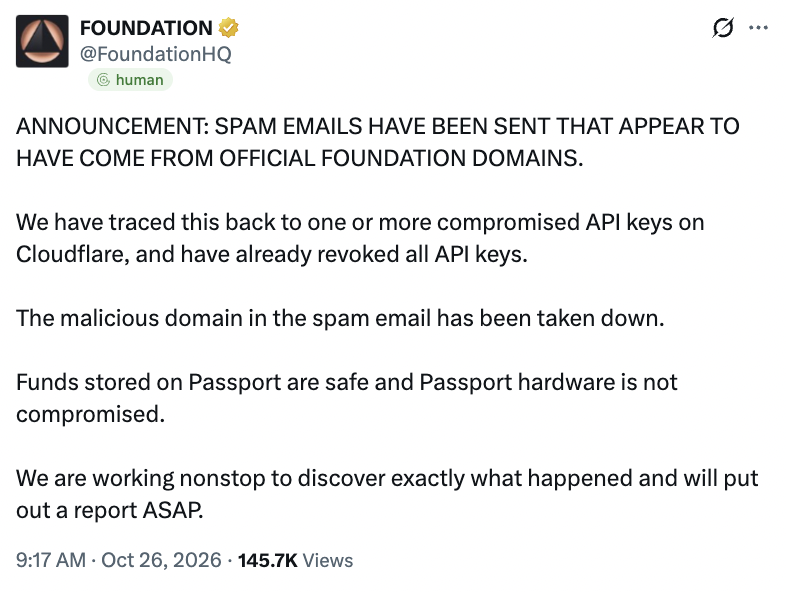
Foundation took to X and famous,
These numbers don’t inform us how many individuals had private info exposed. We are nonetheless figuring out that quantity and can share it as soon as we are able to verify it.
This is as a result of some emails have been despatched a number of occasions or blocked earlier than supply.
How did the attackers orchestrate this?
The investigation additional revealed that the attackers may have accessed private info saved in Foundation’s previous WooCommerce retailer and its present Shopify retailer.
For context, Foundation beforehand used WooCommerce earlier than migrating to Shopify in May. Although the corporate had configured its system to redact buyer info 60 days after an order was shipped, older copies of the information remained in legacy database tables following migrations.
Though the admin dashboard confirmed the knowledge as redacted, the underlying information had not been utterly eliminated. In truth, there’s a chance that different information, together with refunds, deserted carts, and call types, may even have retained private info.
More revelations
Additionally, in its second investigation replace, Foundation disclosed that information containing roughly 5,600 mailing addresses and 5,200 telephone numbers, together with names and electronic mail addresses, have been saved in techniques accessible to the attackers.
However, the corporate can’t verify whether or not each file was accessed, so it’s treating all probably accessible info as exposed.
Now what’s surprising right here is that greater than 5,000 electronic mail addresses that obtained phishing messages weren’t present in its WooCommerce or Shopify buyer information. This signifies that attackers may even have obtained info from exterior sources.
Steps taken by the Foundation
As of now, Foundation has revoked compromised API keys and affected electronic mail credentials. Moreover, it has additionally eliminated the malicious area, cleared queued phishing messages, and brought affected legacy providers offline.
At the identical time, additionally it is rotating keys and secrets and techniques throughout its techniques as a precaution. But what’s fascinating right here is that Foundation has discovered no proof that Passport {hardware} wallets or the personal keys saved on them have been compromised.
This coincided with the FBI not too long ago saying “Operation Blackout.” According to AMBCrypto’s earlier report, this can be a coordinated crackdown on worldwide rip-off compounds that focus on Americans via pretend funding platforms, on-line impersonation, and different fraud schemes.
Final Summary
- The investigation revealed that the attackers may have accessed private info saved in Foundation’s previous WooCommerce retailer and its present Shopify retailer.
- Still, Foundation discovered no proof that Passport {hardware} wallets or the personal keys saved on them have been compromised.